Matt Green has a really excellent post on why Bitcoin isn’t as anonymous as people think, and how to ‘fix’ that problem. If this is something that you’re interested in then his (very) detailed writeup (and link to his paper!) is worth the time and effort.
Category: Links
Categories
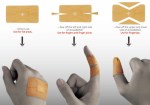

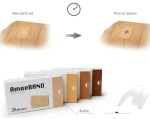
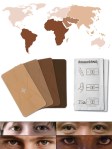
AmoeBAND became a 2012 IDEA Award Finalist by innovating every possible aspect of the plaster (band aid).
The design revisions were:
– Strategic cut-outs shape to fit fingers in such a way that it is easy to bend them and not disrupt the bandage.
– An intelligent dressing material allows you to regularly check wounds from the outside, without upsetting the healing process.“According to research, the when an infection of a wound is detected, the pH value is between 6.5 and 8.5. AmoeBAND’s indicator cross turns purple, alerting the user needs to change it immediately.”
– Since the bandage material used exudes a leather-like feel, availability in different skin-tones helps it blend in, without overly highlighting the injury.
– The packaging has been redesigned to a matchbox style and includes Braille instructions.
Hat tip to designers Tay Pek-Khai, Hsu Hao-Ming, Tsai Cheng-Yu, Chen Kuei-Yuan, Chen Yi-Ting, Lai Jen-Hao, Ho Chia-Ying, Chen Ying-shan, Weng Yu-Ching, and Chung Kuo-Ting
it’s always funny when people improve on something and you look at the innovations and it’s like so fucking obvious what needed to be changed, but yet no one seemingly thought of it until then, yourself included
These are really, really cool, and show what happens when innovation includes not just technology but clear and focused attention to design usability as well.
Tim Wu on my book:
Too much assault and battery creates a more serious problem: wrongful appropriation, as Morozov tends to borrow heavily, without attribution, from those he attacks. His critique of Google and other firms engaged in “algorithmic gatekeeping”is basically taken from Lessig’s first book, “Code and Other Laws of Cyberspace,” in which Lessig argued that technology is necessarily ideological and that choices embodied in code, unlike law, are dangerously insulated from political debate. Morozov presents these ideas as his own and, instead of crediting Lessig, bludgeons him repeatedly. Similarly, Morozov warns readers of the dangers of excessively perfect technologies as if Jonathan Zittrain hadn’t been saying the same thing for the past 10 years. His failure to credit his targets gives the misimpression that Morozov figured it all out himself and that everyone else is an idiot.
What my book actually says:
Alas, Internet-centrism prevents us from grasping many of these issues as clearly as we must. To their credit, Larry Lessig and Jonathan Zittrain have written extensively about digital preemption (and Lessig even touched on the future of civil disobedience). However, both of them, enthralled with the epochalist proclamations of Internet-centrism, seem to operate under the false assumption that digital preemption is mostly a new phenomenon that owes its existence to “the Internet,” e-books, and MP3 files. Code is law—but so are turnstiles. Lessig does note that buildings and architecture can and do regulate, but he makes little effort to explain whether the possible shift to code-based regulation is the product of unique contemporary circumstances or merely the continuation of various long-term trends in criminological thinking.
As Daniel Rosenthal notes in discussing the work of both Lessig and Zittrain, “Academics have sometimes portrayed digital preemption as an unfamiliar and novel prospect… In truth, digital preemption is less of a revolution than an extension of existing regulatory techniques.” In Zittrain’s case, his fascination with “the Internet” and its values of “openness” and “generativity,” as well as his belief that “the Internet” has important lessons to teach us, generates the kind of totalizing discourse that refuses to see that some attempts to work in the technological register might indeed be legitimate and do not necessarily lead to moral depravity.
One of the theoretical frames that I use in my dissertations is path dependency. Specifically, I consider whether early decisions with regards to Internet standards (small, early, decisions) actually lead to systems that are challenging to significantly change after systems relying on those protocols are widely adopted (i.e. big, late, decisions aren’t that influential). Once systems enjoy a network effect and see high levels of sunk capital, do they tend to be maintained even if something new comes along that is theoretically ‘superior’?
I mention this background in path dependency because a lot of the really interesting work in this field was written well before Lessig’s and Zittrain’s popular books (yes: there’s still excellent stuff being written today, but core literature predates Lessig or Zittrain). There’s also a extensive literature in public policy, with one of the more popular works being Tools of Government (1983). Hood, in Tools, that outlines how detectors and effectors work for institutions. Hood’s work, in part, attends to how built infrastructure is used to facilitate governance; by transforming the world itself into a regulatory field (e.g. turnstiles, bridges and roads that possess particular driving characteristics, and so forth) the world becomes embedded with an aesthetic of regulation. This aesthetic can significantly ‘nudge’ the actions we choose to take. This thematic of ‘regulation by architecture’ is core to Lessig’s and Zittrain’s arguments, though there are no references to the ‘core books or sources’ that really launched some of this work in the academy.
This said, while there are predecessors that Lessig and Zittrain probably ought to have spent more time writing about, such complaints are true of practically any book or work that is designed to be read by the public and policy makers and academics. The real ‘magic’ of Zittrain and Lessig (and Morozov!) is that their works speak to a wide audience: their books are not, i would argue, written just for academics. As a result some of the nuance or specificity you’d expect in a $150 book that’s purchased by the other 10 specialists in your field is missing. And that’s ok.
Morozov’s key complaint, as I understand it, is that really important problems arise from how these authors’ books are perceived as what they are not. In other words, many people will not understand that many of the more populist books on ‘the Internet’ are being written by people with specific political intentions, who want their books to affect very particular public policy issues and that, as a consequence, these books and other writings have to be read as political works instead of ’dispassionate academic works’.* Their writings act as a kind of trojan horse through which particular ways of thinking of the world become ‘naturalized’, and the authors are ‘first’ to write on topics largely because of their skill in writing about the present while avoiding elongated literature reviews on the past.
I can appreciate Morozov’s concerns around language framing issues, and around the (sometimes) sloppy thinking of these authors. And I can appreciate Morozov’s critics who see him as being blunt and often similarly failing to ‘show all of his work’. For the public, however, I hope that they don’t necessarily see the very public conflicts between Morozov and his colleagues as necessarily an academic dispute in public so much as an unmasking and contestation of divergent political conceptions of the Internet and of literature more generally.
——-
* I write this on the basis of having attended conferences with American legal scholars working in this area. Papers and reports are often written with specific members of federal sub-committees, Congressional and Senate assistants, or federal/state justices in mind. In effect, these authors are writing for people in power to change specific laws and policies. As such you should always hunt for what is ‘really going on’ when reading most popular American legal scholarship.
Cunningham writes that AeroFS,
If you want access to the best features of Dropbox or one of its many competitors—automated file syncing between computers, a way to automatically keep old versions of your synced files, etc.—but you don’t want to keep your stuff in someone else’s cloud, AeroFS is a promising service. It can provide file syncing for many clients using your own local server (or, for businesses, Amazon S3 storage that you have more direct control over).
These are the kinds of projects that are really interesting to see come to fruition. In British Columbia there is pretty intense law that largely precludes public institutions from storing BC residents’ information outside of the province. The law has created a lot of consternation, especially amongst educators, who believe they can’t use ‘next generation’ tools in their classrooms.
Solutions like AeroFS start to bridge that divide, insofar as more and more ‘cloud’ services can be localized within the province and, as a result, be used by teachers and their students. In effect, such products can satisfy users’ demands while also complying with provincial law. Everyone wins.
So, in line with my previous writing on why I’m skeptical of digital currencies like Bitcoin, Ars Technica has a piece of the newest malware hitting digital currencies:
In another example of the security mantra of “be careful what you click,” at least one Bitcoin trader has been robbed in a forum “phishing” attack designed specifically to ride the hype around the digital currency. The attack attempts to use Java exploits or fake Adobe updates to install malware, and it’s one of the first targeted attacks aimed at the burgeoning business of Bitcoin exchanges.
(…)
This type of attack is de rigeur in the financial world, according to George Waller, the executive vice president of Strikeforce Technologies, a security software firm specializing in two-factor authentication and anti-keylogging software for the financial industry. “Driving people to a site to download malware is one of the most common attacks today,” he told Ars. “You go to a site from a forum and get prompted for Java or Adobe updates—and in the majority of those updates they drop in a keylogger. Since they’re written to get around antivirus scans, AV software is useless against this sort of pervasive malware today.”
To be clear: such attacks are common against a host of perceived high-value targets. They also, however, underscore the real value in linking names, activity-types, purchase behaviour, and other distinctive characteristics to persons’ online economic activity to defray fraud made possible by malware.
On the other hand:
Coupled with this TV functionality, Microsoft’s next-generation Kinect sensor will also play a role in the company’s TV focus. The Verge has learned that the next Kinect will detect multiple people simultaneously, including the ability to detect eye movement to pause content when a viewer turns their head away from a TV.
I really don’t understand this functionality. It sounds like a stupid novelty in the new Samsung Galaxy phone, and I think it’s worse here. Given how many people now “watch” TV with a second screen, is it going to pause every three seconds?
Words cannot express how pissed I would be if turning away from a TV meant that it paused what I was watching. I routinely walk away in dialogue heavy scenes to get a glass of water or whatever, and then return without having missed anything of substance. If I had to change a setting to enable this behaviour (i.e. what I’ve done my entire life) then I’d be annoyed as hell. I think this approach generally presumes that people should be actively just watching what’s on the screen and I really don’t know that many people who focus that hard on screen-based entertainment at home all that often.
Also: as cool as the Kinect is this is the kind of use case that bothers me about the technology more generally. Perpetually having an Internet-accessible series of cameras and microphones is one thing when I can control when they’re on or not: I don’t like the idea of them being ‘on’ when I’m not actively involved in a very specific operation that demands this kind of functionality. And, I mean, if Microsoft implements this there’s no way that advertisers or marketers aren’t going to want the data collected (in ‘aggregate and anonymous’, I’m sure) by the Kinect that’s watching and listening to everything you do within a 15ft radius of your TV.
Google’s intrusion into the physical world means that, were its privacy policy to stay in place and cover self-driving cars and Google Glass, our internet searches might be linked to our driving routes, while our favourite cat videos might be linked to the actual cats we see in the streets. It also means that everything that Google already knows about us based on our search, email and calendar would enable it to serve us ads linked to the actual physical products and establishments we encounter via Google Glass.
For many this may be a very enticing future. We can have it, but we must also find a way to know – in great detail, not just in summary form – what happens to our data once we share it with Google, and to retain some control over what it can track and for how long.
It would also help if one could drive through the neighbourhood in one of Google’s autonomous vehicles without having to log into Google Plus, the company’s social network, or any other Google service.
The European regulators are not planning to thwart Google’s agenda or nip innovation in the bud. This is an unflattering portrayal that might benefit Google’s lobbying efforts but has no bearing in reality. Quite the opposite: it is only by taking full stock of the revolutionary nature of Google’s agenda that we can get the company to act more responsibly towards its users.
I think that it’s critically important to recognize just what the regulators are trying to establish: some kind of line in the sand, a line that identifies practices that move against the ethos and civil culture of particular nations. There isn’t anythingnecessarily wrong with this approach to governance. The EU’s approach suggests a deeper engagement with technology than some other nations, insofar as some regulators are questioning technical developments and potentialities on the basis of a legally-instantiated series of normative rights.
Winner, writing all the way back 1986 in his book The whale and the reactor: a search for limits in an age of high technology, recognized that frank discussions around technology and the socio-political norms embedded in it are critical to a functioning democracy. The decisions we make with regards to technical systems can have far-reaching consequences, insofar as (some) technologies become ‘necessary’ over time because of sunk costs, network effects, and their relative positioning compared to competing products. Critically, technologies aren’t neutral: they are shaped within a social framework that is crusted with power relationships. As a consequence, it behooves us to think about how technologies enable particular power relations and whether they are relates that we’re comfortable asserting anew, or reaffirming again.
(If you’re interested in reading some of Winner’s stuff, check out his essay, “Do Artifacts Have Politics.”)
Looks like some chipmakers might experience some revenue ‘setbacks’ after engaging in antitrust actions:
The case has been ongoing for years, as the European Commission searched the offices of Infineon Technologies AG, STMicroelectronics NV, Renesas Technology Corp. and Atmel Corp. in 2008. In 2009 it investigated companies that make chips for telephone SIM cards, bank cards and ID cards over price-fixing and customer allocation. NXP Semiconductors NV has admitted that it has been involved in the investigations and could be subject to fines.
Should the EU prove that price-fixing is occurring, it can levy fines on companies. While the commission has been trying to negotiated a settlement, those talks have fallen through, which may lead to stiffer fines.
getallthedegrees replied to your post: must force myself to stop eating pad thai
I’ve been told your supervisor does the asking, though you have input. But that might just be my department. However, for my MA my supervisor did the asking but asked who I wanted. So I dunno??Sorry – to clarify, when I said “committee” I was including supervisor. Because I don’t yet have anyone formally signed on. Three years into the PhD. Despite semi-frequent discussions of research and stuff with three or four faculty members. And it’s really hard to track anyone down unless there’s a talk or something where I can chase them afterwards and beg for a meeting time.
Forgive my ignorance of econ programs, but how did you get through your comps without a formal supervisor? Unless, this means you didn’t do comps? Do you do quals instead? How is your program structured?
I was told that I’m supposed to formally ask who I want to be my supervisor, and should really be thinking about it soon (September at the latest) according to the grad advisor. In my program you don’t ask formally until you do candidacy* (after you finish your coursework), but since I’m not able to take the remaining classes I need over the summer I’ll be doing candidacy work sort of unofficially.
*In my program (and I think most programs in my institution) we take more classes than most (eight, rather than four or six), and skip the comps/quals process and do candidacy instead. Candidacy is the first three chapters of your dis, so intro, lit review and methodology (~ 80-100 pages) which you defend in an oral exam.
Okay so hopefully this isn’t overshare but here’s how my program (and, I think, most econ programs) works:
- Eight months of general coursework (three per term for two terms). Everyone takes this together.
- Two comp exams. Everyone takes these together. They cover all of macro and micro theory. One or two people get kicked out.
- Another eight months of coursework, this time with four per term for two terms. This is where specialization happens.
- Four months of writing a paper. This is supposed to get you familiar with the process but is almost always a failure.
- Twelve months of preparing for prospectus defence. This is where I am now. Typically a big chunk of your thesis gets written here.
- Prospectus defence and assembling a committee. Including the prof who’s formally your supervisor.
- Twelve months of preparing for the job market. Your best paper gets super polished as your Job Market Paper around this point.
- Four months of job market. In here, you’re also finishing your thesis. But really it’s your Job Market Paper that matters more than the actual thesis.
- Four months of finishing up the thesis, getting a job, and defending the thesis.
- Graduating and very very hopefully progressing to gainful employment.
So the big paper I’m currently working on right now will very hopefully be my Job Market Paper. Other projects I’m working on might end up in my thesis. At least one is getting published and isn’t going to be part of my job application at all because it’s not economics.
And yeah accordingly I really really need to put together a committee to formally supervise my actual thesis. And I don’t know how much coldness is par for the course or at what point it actually becomes a strong negative signal.
That’s….a different structure from any other I’ve seen. I’ve the good fortune of entering the program with a supervisor (you can switch later, if you want). He’s helped pay a bunch of my bills + general guidance.
He’s also taken most of the work out of finding people for the committee: we had a meeting and went back and forth on names, and then he rounded folks up. It’d have been super awkward to do this myself, given that I tend not to know people in the program terribly well (and they tend to look at me funny, not quite knowing what it is that I actually do as an academic).
Peter Fleischer has a good summary piece on the (miserable) state of online privacy policies today. As he writes:
Today, privacy policies are being written to try to do two contradictory things. Like most things in life, if you try to do two contradictory things at the same time, you end up doing neither well. Here’s the contradiction: should a privacy policy be a short, simple, readable notice that the average end-user could understand? Or should it be a long, detailed, legalistic disclosure document written for regulators? Since average users and expert regulators have different expectations about what should be disclosed, the privacy policies in use today largely disappoint both groups.
(…)
The time has come for a global reflection on what, exactly, a privacy policy should look like. Today, there is no consensus. I don’t just mean consensus amongst regulators and lawyers. My suggestion would be to start by doing some serious user-research, and actually ask Johnny and Jean and Johann.
I entirely, fully, wholeheartedly agree: most policies today are absolute garbage. I actually read a lot of them – and research on social media policies will be online and available soon! – and they are more often than not an elaborate act of obfuscation than something that explains, specifically and precisely, what a service does or is doing with the data that is collected.
The thing is, these policies don’t need to be as bad as they are. It really is possible to bridge ‘accessible’ and ‘legalese’ but doing so takes time, care, and effort.
And fewer lawyers.
As a good example of how this can be done check out how Tunnelbear has written their privacy policy: it’s reasonably accessible and lacks a lot of the ‘weasel phrases’ you’ll find in most privacy policies. Even better, read the company’s Terms of Service document; I cannot express how much ‘win’ is captured in their simultaneously legal and layperson disclosure of how and why their service functions as it does.
 Excited Pixels
